


Cybersecurity has become a major topic of global discussion among businesses across all sectors over the past week, as personal consumer data entrusted to service providers has been put at risk, with some cases reportedly involving unauthorised access by third parties.
Thai Airways was among several airlines that issued statements acknowledging a passenger data breach affecting approximately 60,000 customers. The incident was primarily linked to a data leak at Amadeus IT Group S.A., a provider of reservation and passenger service systems for many airlines.
Reports of cyber-attacks affecting several overseas banks also prompted the Bank of Thailand to urge commercial banks to strengthen their cybersecurity measures last week.
Although these incidents have yet to directly affect businesses and consumers in Thailand or cause significant financial damage, they still raise important questions about how well prepared Thailand is to address such cyberthreats.
MOUNTING CYBERTHREATS
Thailand recorded an average of 3,132 cyber-attacks per organisation per week in 2025, up 14% from 2024. The figure was 8% higher than the Asia-Pacific average and 59% above the global average, according to Check Point Software Technologies.
Chanvith Iddhivadhana, country manager for Thailand at Check Point Software Technologies, said Thailand's role as a regional logistics, automotive and manufacturing hub made it particularly vulnerable to supply-chain attacks.
He identified four major cybersecurity threats facing Thailand in 2026: vulnerabilities arising from poorly integrated IT and operational technology systems, AI-powered attacks, supply-chain disruptions and a shortage of skilled cybersecurity professionals.
Manufacturers face growing risks from outdated industrial systems and inadequate network segmentation, while agentic AI enables attackers to automate reconnaissance and social engineering at unprecedented speed and scale.
"A single breach at a third-party provider could trigger cascading disruptions across the manufacturing ecosystem," he said.
Mr Chanvith said Thailand's biggest cybersecurity challenge was no longer awareness but the effective deployment and integration of modern defences across fragmented legacy systems.
According to FortiGuard Labs, its threat monitoring dashboard recorded 24 million blocked cyber-attacks in Thailand over a 30-day period, highlighting persistent threats to businesses and public institutions. The dashboard also recorded nine attacks per second and 140 active outbreaks.
Technology and government were the most targeted sectors, each recording 1.6 million detections. Food and beverage followed with 878,000, education with 854,000 and manufacturing with 766,000.
According to Adrian Hia, managing director for Asia-Pacific at Kaspersky, a Kaspersky survey revealed that 87% of small and medium-sized businesses in Asia-Pacific encountered cybersecurity incidents over the past year.
Vietnam recorded the highest rate in the region, at 97%, followed by Malaysia (95%), Indonesia (92%) and India (87%). Thailand and China reported rates below the regional average, at 82% and 67%, respectively.
Chatchai Komrangded, head of solutions architecture at AWS Thailand, said that as technology advances, the time between a vulnerability becoming public and being exploited is shrinking rapidly.
"AI is speeding up how quickly vulnerabilities are found, so a security check from a year ago may no longer reflect today's risk," Mr Chatchai said.
As companies adopt generative AI, they need to treat compliance and governance as always-on requirements, not as a once-a-year check. Defenders need to move just as fast, he added.
Security in the cloud is a shared responsibility. Under the shared responsibility model, AWS secures the infrastructure, from the chip level up to the services customers use, Mr Chatchai said.
Customers are responsible for how they configure those services and protect their own data, identities and applications.
The measures that matter most are strong identity and access controls, continuous monitoring and testing, and clear roles between providers and customers.
"On our side, we use automated reasoning, which applies mathematical logic to prove that access policies and AI outputs follow a customer's rules every time," Mr Chatchai said.
The company also uses the scale of its network to spot new threat patterns early and roll out protections, either directly or through its services.
On the customer side, the company provides tools that help customers keep pace. AWS Continuum, for example, detects vulnerabilities, ranks them by priority and proposes fixes so teams can patch faster.
In Thailand, AWS works closely with the National Cyber Security Agency (NCSA).
"Together, we built the Thailand Secure Landing Zone, which helps organisations launch cloud workloads with secure-by-default controls aligned with NCSA standards," Mr Chatchai said.
Vilaiporn Taweelappontong, deputy managing director at Microsoft Thailand, said cloud services increasingly support essential functions across government, business and critical sectors.
Cybersecurity readiness must therefore be measured not only by the ability to prevent attacks, but also by how effectively organisations detect and contain threats, maintain critical operations and recover safely, Ms Vilaiporn said.
The Microsoft Digital Defense Report 2026 identifies three priorities: protect identities, respond faster and build resilience.
"At Microsoft, security is a continuous commitment. We combine global threat intelligence, hyperscale cloud and AI-enabled security to help organisations manage exposure, protect identities and respond to threats at machine speed, with human accountability," Ms Vilaiporn added.
At the same time, security is a shared responsibility. Microsoft secures the underlying cloud infrastructure, while customers remain responsible for protecting their accounts, data and systems, depending on the services they use.
Essential security practices include phishing-resistant multifactor authentication, least-privilege access, prompt patching, particularly for internet-facing systems, and regular employee training.
She said organisations should also follow threat advisories from technology providers and national agencies and act quickly when new vulnerabilities or attack campaigns are identified.
As cloud services become more integral to national infrastructure, additional safeguards should be risk-based, proportionate and tailored to their role.
Regulation can establish a strong baseline, but no organisation can address today's cyber-risks alone. Sustained collaboration among government, regulators, cloud providers and critical-sector operators is essential to maintain critical services and public trust, Ms Vilaiporn noted.
Saruj Thipsena, Thailand country manager at Google Cloud, said that as cybercriminals are using AI tools to launch attacks at machine speed, manual defence is no longer enough; organisations also need to leverage AI agents to strengthen their defences.
This means that cloud security must be built directly into the foundation rather than treated as an afterthought or an add-on, Mr Saruj said.
He said Google Cloud protects Thailand's critical infrastructure by embedding security by design and zero-trust principles into every layer of its cloud infrastructure -- from custom silicon to its global network.
In this AI-driven, human-led approach, AI security agents work alongside human defenders to autonomously triage threats, investigate root causes and generate validated software patches -- shrinking response and remediation times from weeks to minutes before hackers can exploit them.
Looking at highly regulated sectors such as banking, the biggest shift needed across critical infrastructure is moving from point-in-time compliance checklists to continuous, AI-driven resilience, Mr Saruj said.
Just as banks run regular financial stress tests, critical infrastructure providers must conduct continuous adversarial testing, automated risk validation and real-time threat intelligence sharing across the public and private sectors.
"At Google Cloud, we call this 'shared fate' -- we don't just provide cloud infrastructure; we partner closely with Thai enterprises and regulators to embed machine-speed, AI-powered defence directly into the nation's digital backbone," Mr Saruj said.
RED ALERT
Kitti Kosavisutte, honorary advisor to the Thailand Banking Sector Computer Emergency Response Team (TB-CERT), established by the banking sector under the Thai Bankers' Association (TBA) as a central cybersecurity coordination platform, said the Thai banking sector was placing greater emphasis on AI agents that operate autonomously around the clock to enhance its ability to detect and respond to cyberthreats.
Banks are preparing to improve their AI model training techniques to make these systems more sophisticated and better equipped to identify potential attacks and respond more quickly.
TB-CERT is also facilitating information sharing among banks, including intelligence on hacking techniques and emerging cyberthreats, to strengthen financial institutions' preparedness and enable better coordination of defensive measures.
"Despite persistent attempts to breach banking systems, no commercial bank has suffered any damage so far. TB-CERT is making every effort to protect the banking sector amid a global rise in cyberthreats, particularly following a series of reports about cyber incidents over the past one to two weeks," he said.
However, Mr Kitti noted that some media reports contained inaccurate information or linked unrelated incidents to cyber-attacks and financial crime, potentially causing unnecessary public concern and inadvertently lending credibility to scammers.
Mr Kitti cited a recent incident in Japan, saying it was caused by telecommunications system problems rather than a cyber-attack. Such inaccurate reporting could therefore create the misleading impression that hackers had successfully breached financial systems when, in fact, they had not.
Meanwhile, Payong Srivanich, chairman of the TBA, said TB-CERT serves as a central cybersecurity coordination platform, facilitating information sharing across the banking industry to safeguard the domestic banking system.
Beyond the banking sector, TB-CERT also coordinates with relevant agencies, including the Bank of Thailand (BoT) and the National Cyber Security Agency (NCSA), to monitor and detect cyberthreats that could affect multiple industries.
"Through concerted efforts to prevent cyberthreats, the TBA believes it can maintain public confidence and hopes the situation will not trigger public panic or a rush to withdraw cash," Mr Payong said.
The central bank has also instructed financial institutions to tighten cybersecurity controls and improve incident-reporting procedures. Banks are required to report suspicious activities and potential cyber-attacks daily to facilitate closer monitoring, faster assessments and information sharing among financial institutions and the central bank.
In response to the central bank's requirements, banks have intensified their cyberthreat defences through a proactive, 24/7 monitoring approach.
They have also upgraded security measures to strengthen cybersecurity standards, safeguard customers' funds and data, and maintain public confidence in financial transactions.
STRENGTHENING DEFENCES
The Securities and Exchange Commission (SEC) is stepping up its cybersecurity oversight, urging businesses in the capital and digital asset markets to strengthen safeguards amid growing cyberthreats.
SEC deputy secretary-general Anek Yooyuen said the regulator has been closely monitoring cyberthreats emerging overseas that could potentially affect critical systems and services.
The SEC prioritises ensuring that businesses under its supervision are adequately prepared to respond to potential threats, maintain service continuity and minimise risks to investors and the capital market.
"The SEC is closely monitoring the evolving cyberthreat situation and continues to coordinate with business operators and relevant agencies," he said.
The regulator has sent a letter to businesses under its supervision, including the Stock Exchange of Thailand (SET) and companies in the SET Group, urging them to step up their cybersecurity measures.
The letter calls on operators to strengthen cyberthreat monitoring and safeguards, review the adequacy of existing security measures and improve their readiness to respond to potential incidents in line with their level of risk.
It also urges boards of directors and senior executives to give priority to information technology and cybersecurity risk management, stressing that responsibility should not rest solely with IT departments.
Boards and senior executives are ultimately responsible for setting policies, allocating resources, overseeing the effectiveness of security controls and ensuring that any weaknesses are addressed promptly, said Mr Anek.
The SEC has also established supervisory procedures to manage cyber incidents that could affect regulated businesses. These include monitoring and assessing incident severity, coordinating with relevant agencies and implementing appropriate response measures.
The framework is designed to ensure that the regulator can take timely and proportionate action based on the severity of each incident.
The SEC also stressed that businesses must strictly comply with cybersecurity rules and requirements to ensure their systems remain resilient, enable timely responses to threats and minimise potential disruption to investors and services.
Operators are also required to report to the SEC on measures taken to strengthen their cybersecurity in response to the warning.
ENDLESS BATTLE
Safeguarding internet-based business operations from cyber-attacks has become an essential and constant challenge for companies of all sizes, as cybercriminals continue to develop increasingly sophisticated methods of penetrating IT systems, according to the Federation of Thai Industries (FTI).
"Attackers are always one step ahead. Defending against them is a continuous process with no finish line," said Montri Mahaplerkpong, vice-chairman of the FTI.
Mr Montri said many businesses now view IT systems as a significant operational burden due to their rising costs. However, companies are compelled to invest heavily in cybersecurity as cyberthreats become more severe and difficult to contain.
Many firms have adopted dual-system operations, running both on-premises servers and cloud-based platforms simultaneously to enhance resilience.
They also implement regular data backup plans on a weekly and monthly basis to minimise disruptions in the event of an attack.
Strong cybersecurity measures are no longer the preserve of large corporations.
"Small and medium-sized enterprises [SMEs] also have to invest in cybersecurity. Every business, regardless of size, is now affected," Mr Montri said.
He called on the government to make greater use of its intelligence capabilities to provide warnings and threat assessments of cybercriminal activities.
Such support is particularly important for SMEs, which often lack the resources to monitor global cyberthreats.
Mr Montri also urged the state to play a stronger role in strengthening cybersecurity infrastructure and information-sharing networks through mechanisms such as the Joint Standing Committee on Commerce, Industry and Banking.
RISING CONCERN
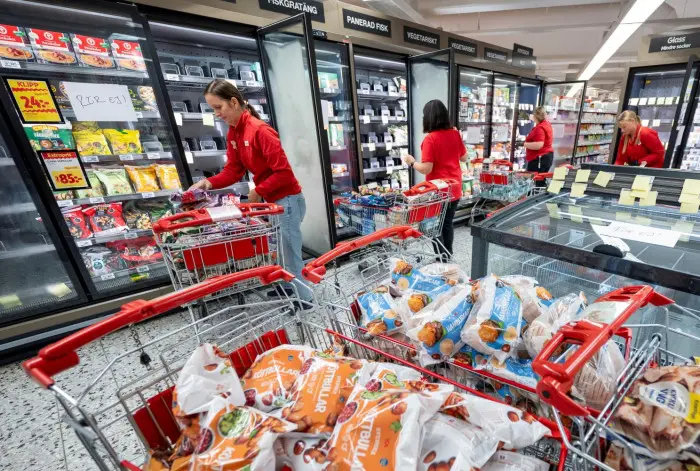
Growing concerns over cyberthreats have been fuelled by a report from Sweden, where a supermarket operator was reportedly affected by a cyber incident that caused refrigeration temperatures to surge to 50°C, resulting in food spoilage and raising suspicions of cyber sabotage.
Mr Montri said members of the FTI, particularly those in the food processing and agricultural sectors, have become more alert to cybersecurity risks and are investing in more advanced cyber protection technologies.
Thailand's agriculture and food industries, which generated economic value of around 1.2 trillion baht during the first nine months of the year, have experienced sluggish performance, with output contracting by about 5% year-on-year, Mr Montri said.
Ongart Kittikhunchai, president of the Thai Food Processors' Association, said Thai operators had already been holding regular risk assessment meetings before news emerged about cyber-attacks targeting refrigeration systems at European retailers.
These meetings addressed preventive measures to mitigate company data leaks, minimise human error and prevent data theft.
Personally, he views the European hacking incidents as a catalyst that has significantly heightened cybersecurity concerns.
His company holds regular risk-preparedness meetings. While previous agendas focused on economic, financial and business risks, cybersecurity has now become a prominent concern.
The company is currently updating its operational systems by implementing new passcodes to enhance security and is discussing the safety of financial transactions with banks.
He added that last week, his company met with its suppliers to review risk-prevention measures, focusing on financial safeguards, corporate financial systems and fund transfer processes between the company and its customers.
Regarding production, he noted that as more manufacturing equipment connects to online systems, there is a growing risk that hackers could leverage AI to facilitate cyber-attacks.
Thai companies are increasing their focus on technology, especially by adopting AI to support business and industrial operations.
He said companies will likely address cybersecurity alongside AI adoption and place greater emphasis on it in next year's technology investment budgets.
The Mall Group has also increased the frequency of its cybersecurity checks, said Voralak Tulaphorn, chief marketing officer at The Mall Group.
She added that the company's refrigeration systems are not fully connected to the internet.
Overall, she views internet-connected equipment as offering businesses benefits, while stressing the importance of risk assessments that consider factors such as vulnerability to natural disasters or cyber-attacks.
"Being online can be advantageous for certain business operations, but it is not necessary for every aspect of business," Ms Voralak said.
Suny Sidik, chief commercial officer of Central Food Wholesale Ltd, said the company has a contingency plan to handle emergencies and unexpected circumstances.
She confirmed that Go Wholesale, a nationwide food wholesale chain, maintains adequate product supplies to fulfil customer demand in all situations.
Additional report by Lamonphet Apisitniran and Kuakul Mornkum